Secrets
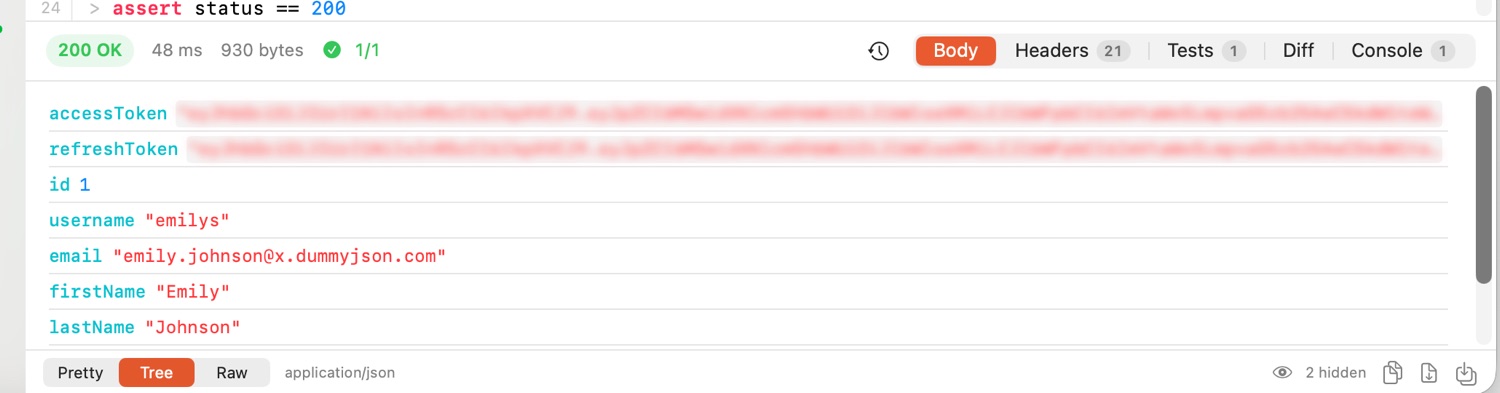
Wrap anything private in secret(...). It is masked in output, in reports and in the app, and it belongs in environment.local.stamp, which the app keeps out of git.
# environment.local.stamp, which git ignores
vars environment=prod {
  apiKey = secret("live-key-goes-here")
  dbPassword = secret(getenv("DB_PASSWORD"))
}
stamp run . --show-secrets # unmask, for local debugging onlyIn the app: Request ▸ Show Secrets (⇧⌘H) toggles, and the inspector has a Shared / This Mac switch that decides which file a variable is written to. Values from save always go to the local file.